Security Assurance
End-to-end assurance for government and enterprise systems — risk assessments, control reviews and accreditation evidence that stands up to scrutiny, from discovery through to executive reporting.
I'm Haidar Rashid. I share practical perspectives on cyber risk, resilience and leadership, shaped by over a decade across central UK government, enterprise and community organisations.
Expertise
Turning cyber risk into decisions your board can act on.
Background
A decade across UK government and industry — from discovery through to executive reporting.
Community outreach
Cyber security is a community effort — I co-founded CyBeds CIC and give back at a local Citizens Advice.
Live from the radar
Each blip is a piece of writing I am still thinking about — hover one on the screen, or take the short route below.
01 — Areas of expertise
End-to-end assurance for government and enterprise systems — risk assessments, control reviews and accreditation evidence that stands up to scrutiny, from discovery through to executive reporting.
Regulatory requirements translated into roadmaps your boards can approve and your teams can deliver.
Risk posture and governance maturity reported in language executives act on — no 200-page PDFs nobody reads.
Security management plans, policy alignment and stakeholder liaison for central UK government programmes.
Incident response readiness and community resilience planning — informed by national-level work with a UK government department.
Mentoring and frameworks that leave your own people stronger — I've built and led assurance teams across the public and private sector.
02 — Case studies
Selected examples of my assurance and resilience work, with client names and identifying details withheld. I focus on my contribution, without claiming measured client results.
Central UK government
Enterprise · Consultancy
National resilience · UK government department
Capability building
Between the lines
Move your cursor across the dark to light them — on a phone, drag your finger, or reveal them all at once.
“Can we still trade on Monday?”
“Who owns this risk — by name?”
“What would you tell the board if nothing were broken?”
“Which control would you notice if it went quiet?”
“What would you fix first if I handed you the budget?”
03 — Cyber readiness check
Nothing is stored, sent or emailed — this is a scratchpad, not a form. Answer as your organisation is today, not as you would like it to be.
Sometimes
Sometimes
Sometimes
Sometimes
Sometimes
Where you stand
15/25
Foundations with gaps to address
Your answers suggest some useful foundations and some uneven areas. Start with the priority below rather than tackling everything at once.
Close your most important gap
Bring leadership together to agree the three cyber risks that would most disrupt your organisation, then name an owner for each.
A reflection on your answers, not an audit or certification.
Discuss your prioritiesWorth reading next
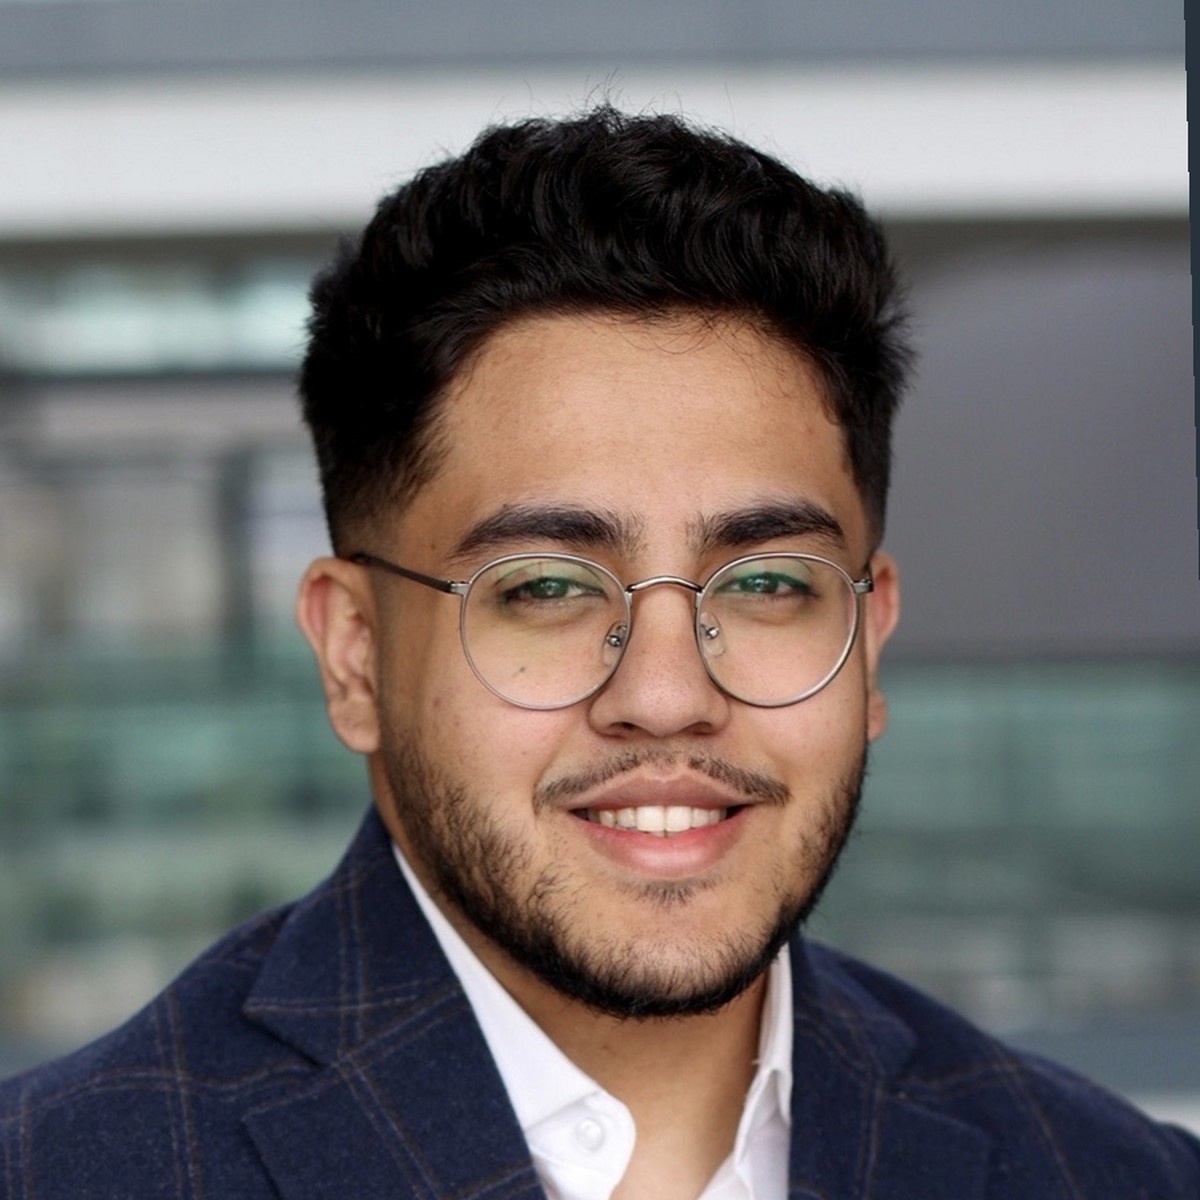
Haidar Rashid
PriCSP · MCIIS
04 — About
I've spent over ten years in information and cyber security across central UK government and enterprise — including Big 4 consulting on government engagements, and leading cyber assurance delivery in large consultancies.
As Principal Security Consultant at BAE Systems Digital Intelligence, I lead cyber assurance and risk engagements on complex programmes — alongside a cyber security secondment with a UK government department, contributing to national resilience. That experience reinforced my belief that people are at the heart of cyber security — the best assurance only lands when it connects with the humans behind the decisions. So everything I deliver is specific, prioritised and written for people.
Outside client work, I co-founded CyBeds CIC to open up cyber careers in Bedfordshire and serve as a Trustee at a local Citizens Advice, leading on cyber security. I previously served as an elected education governor for a local education trust.
 PriCSP · Cyber Security Governance & Risk ManagementUK Cyber Security Council
 MCIIS · Full Member (Accredited)Chartered Institute of Information Security
05 — Community
Co-founder
I co-founded CyBeds, a Community Interest Company breaking down the barriers to cyber careers in Bedfordshire — for students, career changers, experienced practitioners, charities and small businesses alike. The goal is simple: create opportunities, build capability and strengthen cyber resilience across our communities.
Cyber Social
Connecting people, building networks and creating a supportive community.
Cyber Pathways
Helping individuals start and progress their cyber security careers.
Cyber Green
Promoting sustainability and responsible practice across cyber and technology.
Cyber Clinics
Practical guidance for individuals, charities and small organisations.
Cyber Guardians
Community awareness, education and resilience initiatives.
Trustee
As a Trustee I lead on cyber security — helping a local charity give free, independent advice to the community while keeping its own technology and data safe and its services open to everyone.
Visit Citizens AdviceGovernor
I previously served as an elected education governor for a multi-academy education trust, with responsibility for its secondary academies — plus school engagement through Inspiring the Future.
06 — Experience

Leading cyber security assurance and risk engagements across complex central UK government programmes — owning outcomes from discovery through to executive reporting.

Contributing to national cyber resilience through stakeholder coordination, incident awareness and assessment of sector vulnerabilities.

Led assurance delivery for enterprise and public-sector clients, presented compliance roadmaps to executive boards and mentored consultants.
Delivered cyber security consultancy for government, defence and private-sector clients — risk management, security assurance and compliance with contractual security requirements.
Owned the company's personnel security — managing vetting and security clearances for staff working on sensitive contracts.

Managed assurance for high-value government contracts, developed Security Management Plans and reported risk exposure to executive boards.
Managed a small team of five delivering audits, governance reviews and assurance advice across central government — setting direction, assuring quality and developing people.
Advised eight departments on data protection and privacy risk — shaping policy, supporting DPIAs and helping senior leaders make confident, compliant decisions.
Owned information governance frameworks and reporting — improving how information was handled, shared and protected across the organisation.
Started my cyber career on the front line — supporting security accreditation and incident management while learning how government security really works.
07 — Speaking & conversations
I’m always open to a useful conversation — whether you’re planning a cyber event, exploring a difficult issue or simply want to compare notes with another practitioner.
Find a time on CalendlyPanels, podcasts, roundtables and events exploring cyber risk, resilience, governance and careers.
Informal conversations with practitioners, community leaders and people finding their route into cyber.
Ideas and collaborations that can strengthen cyber awareness, inclusion and resilience where it matters.
08 — Contact
Follow what I’m sharing, invite me to contribute, or send a note if there’s a cyber security issue worth unpacking together.
Cyber. Innovation. Community.
Haidar Rashid
All about innovating & securing
Cyber security governance and risk management — practical advice, assurance and strategy for people and organisations.
Click to open
London